Pulumi Alternatives in 2026
Six alternatives to Pulumi, ranked for backend teams, with the same Postgres database in each and a verdict on when to pick which.
The best Pulumi alternative for backend teams in 2026 is Encore, an infrastructure from code tool: your TypeScript or Go application declares the Postgres databases, Pub/Sub topics, buckets, cron jobs and secrets it uses, and Encore runs the databases, topics and buckets locally and provisions those resources in your own AWS or GCP account. Cron jobs are Encore platform Managed: the schedule runs on the platform, not as EventBridge or Cloud Scheduler in your account. There is no separate infrastructure program, no state backend and no pulumi up. If you want to stay with infrastructure as code, Terraform and OpenTofu have the largest ecosystems, AWS CDK keeps a general-purpose language on AWS, and Crossplane suits teams that already run Kubernetes as their control plane.
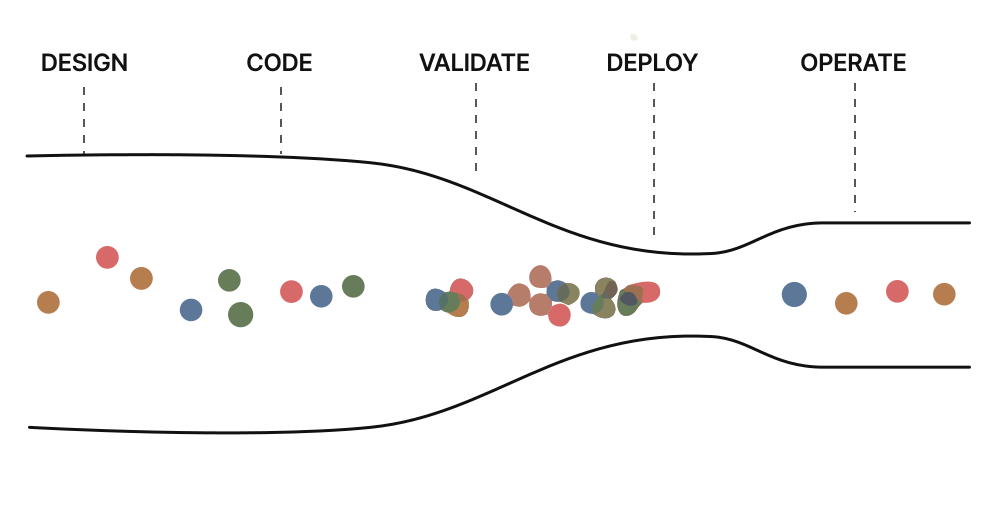
Pulumi gave infrastructure a general-purpose language, with types, loops and packages. What it kept is the split: the infrastructure is still a second program with its own state and its own deploy, and a feature that needs a new queue waits on that second change. Research into AI-native delivery shows that split getting more expensive as agents write more of the application code, because code output has grown much faster than how often teams ship:
What are the best Pulumi alternatives?
Why is Encore the top Pulumi alternative for backend teams?
Encore is infrastructure from code, with a platform that automates the infrastructure from local development to cloud deployment. Instead of describing application architecture in a separate infrastructure program, you declare services, APIs, and infrastructure resources in application code. Encore uses those declarations to run the application locally, validate it, and provision the infrastructure it needs in your own AWS or GCP account, without giving up control over how each environment is set up.
On a single resource, a Postgres database in Pulumi is a typed object in a program with its own state, while in Encore the application declares what it needs:
Pulumi
const db = new aws.rds.Instance("app-db", {
  engine: "postgres",
  instanceClass: "db.t3.micro",
  allocatedStorage: 20,
  dbName: "app",
  password: config.requireSecret("dbPassword"),
  skipFinalSnapshot: true,
  // ... plus the stack, state, and pulumi up
});
Encore
const db = new SQLDatabase("orders", {
  migrations: "./migrations",
});
The same Postgres database, written as a Pulumi program and declared in Encore.
It looks like a trade-off between configurability and simplicity, but the level of control is the same, with each setting kept in its own place. Encore, through static analysis (a fancy way of saying it reads your code without running it), infers what it needs from the declaration: the database, its migrations, which services use it, and the IAM that follows from that. How it runs, such as its instance size, storage, networking, and backups, is abstracted into your environment configuration, which stays outside the code you (or an agent) write. That lets the same code run locally, in preview environments, and across different cloud providers.
Working with agents

encore run. The same declaration provisions an S3 bucket (or Cloud Storage on GCP) in production, so what runs locally matches what ships.A Pub/Sub topic, an object storage bucket, or a cron job (and the other primitives Encore supports) works the same way. When an agent adds one:
- The infrastructure ships in the same pull request as the feature, with no separate Pulumi program of subnets, security groups, and IAM for an agent to write and a reviewer to read line by line.
- From the first
encore run, the change runs against real infrastructure locally and in each preview environment, so an agent (or human) can verify how it behaves end to end before it reaches production. Cron jobs are Encore platform Managed and only run on schedule in deployed environments, not locally or in previews. - The same declaration drives every environment, so what the agent verifies locally is what runs in production.
- The agent reads any failure in the traces, logs, and type errors and fixes it before the change ever becomes a pull request.
- Capacity, networking, backups, and credentials stay in environment configuration the agent cannot touch, so the guardrails a platform team sets hold however many changes land.
Best for
Encore is the strongest fit for teams building backend services on AWS or GCP that want AI agents to ship features together with the infrastructure they need, inside the guardrails set for production.
Adopting it also assumes your existing Pulumi program can stay in place, still managing the shared, org-level, or unsupported infrastructure it already handles while Encore takes the application resources it supports. Encore connects to databases you already run, such as RDS and Cloud SQL, so the two run side by side.
Learn more about how Encore automates infrastructure
Run in your terminal to get started locally.
Is Terraform a better choice than Pulumi?
Terraform is the tool Pulumi set out to improve on, and it remains the default infrastructure as code, with the largest provider ecosystem of any option here. You describe resources in HCL, a configuration language of its own, and Terraform plans and applies them against a state file it maintains. The same Postgres database is a block of HCL:
resource "aws_db_instance" "users" {
  identifier        = "users-db"
  engine            = "postgres"
  instance_class    = "db.t3.micro"
  allocated_storage = 20
  db_name           = "users"
  username          = var.db_username
  password          = var.db_password
  # ... plus networking, IAM, secrets
}
Working with agents
An agent generates HCL as fluently as it generates a Pulumi program, but the change stays inert until someone runs terraform plan and terraform apply, and it runs against shared state a careless edit can corrupt. There is no way to stand the real infrastructure up locally and check the change in the dev loop, so the apply, usually against a live environment, is the first test. Moving from Pulumi to Terraform trades a general-purpose language for a bigger ecosystem, but the separate-program-and-state workflow is the same.
Best for
Terraform fits teams that want the broadest provider coverage and the largest ecosystem of modules and examples, and are comfortable staying in HCL rather than a general-purpose language. It is source-available under the BSL license now rather than open source, which is what led to the OpenTofu fork, and the workflow is unchanged from what you have in Pulumi: a separate configuration behind its own state and its own apply.
Is OpenTofu a good Pulumi alternative?
OpenTofu is a fork of Terraform, created after HashiCorp moved Terraform to the source-available BSL license in 2023. It is an open source MPL 2.0 project under the Linux Foundation and a CNCF Sandbox project since April 2025. It keeps HCL, the provider protocol, modules, and the plan-and-apply workflow, so existing .tf files, providers, and state work with little or no change. The same database is the same .tf:
# The same .tf as Terraform, unchanged: providers and state carry over
resource "aws_db_instance" "users" {
  identifier     = "users-db"
  engine         = "postgres"
  instance_class = "db.t3.micro"
  # ... plus storage, credentials, networking, IAM
}
Working with agents
An agent works with OpenTofu the same way it would with Terraform, generating HCL fluently, but the change stays inert until someone runs tofu plan and tofu apply, and it runs against the same shared state a careless edit can corrupt. There is no way to stand the real infrastructure up locally and check the change in the dev loop, so the apply itself, usually against a live environment, is the first test. The split between application code and a stateful infrastructure pipeline is structural, and an open source license does not close it.
Best for
OpenTofu is the least disruptive move for teams that want the Terraform model without its source-available license, and it has since added features of its own, such as built-in state encryption and OCI-based provider registries. Like Terraform, it keeps HCL and state, so an application change can still require a separate infrastructure change.
If OpenTofu is already your current tool, see OpenTofu alternatives in 2026 for how it compares with the others.
When should you use AWS CDK instead of Pulumi?
 AWS CDK
 lets you define AWS infrastructure in TypeScript, Python, Java, C#, or Go, using constructs that bundle several resources into reusable components. Like Pulumi, it gives you a general-purpose language, but it synthesizes that code into a CloudFormation template, which AWS then deploys and tracks as a stack.
const db = new rds.DatabaseInstance(this, "Postgres", {
  engine: rds.DatabaseInstanceEngine.postgres({
    version: rds.PostgresEngineVersion.VER_16,
  }),
  instanceType: ec2.InstanceType.of(ec2.InstanceClass.BURSTABLE3, ec2.InstanceSize.MICRO),
  credentials: rds.Credentials.fromGeneratedSecret("postgres"),
  vpc,
});
Working with agents
Constructs are ordinary code, so an agent authors them fluently, but the code is only the first phase. It has to be synthesized to CloudFormation and deployed with cloud credentials before anything exists, and the agent has to reason about a two-step path, source to template to stack, that it cannot see from the source alone. There is no local run against real infrastructure to validate the change first.
Best for
CDK fits teams committed to AWS who want a general-purpose language, like Pulumi, but tied to CloudFormation and its stacks rather than a separate state backend. It stays inside AWS, though, with infrastructure in a separate app and no path to GCP or Azure, so it is a narrower choice than the multi-cloud program Pulumi gives you. Its first major version reached end of support back in 2023, but version 2 ships weekly and is actively maintained, so the reason to weigh it against Pulumi is the AWS lock-in, not any lack of upkeep.
Is SST a good Pulumi alternative?
SST is a framework for building and deploying full-stack applications, mostly on AWS, with higher-level components, resource linking, and a console for inspecting what you shipped. It runs on Pulumi with Terraform providers underneath, which is what lets it reach past AWS and past CloudFormation's stack limits, but it wraps that in an app-developer experience.
// sst.config.ts
const vpc = new sst.aws.Vpc("MyVpc");
const db = new sst.aws.Postgres("MyDatabase", { vpc });
Working with agents
Infrastructure and application code live in one TypeScript project, so an agent editing an SST app touches both at once, and the components are declarative and easy to generate. Nothing provisions until sst deploy runs, though, and because it sits on Pulumi, the same state and drift concerns apply, so the change still passes through a separate deploy before it is real. There is no local run against real infrastructure to check it in the dev loop first.
Best for
SST fits TypeScript teams building serverless-heavy applications on AWS that want less infrastructure boilerplate and a tighter link between app and cloud. It is the closest of these tools to putting infrastructure beside application code, but it keeps a separate sst.config.ts, the Pulumi state backend underneath, and a deploy step, and it stays oriented around AWS. Its core team moved most of its focus to OpenCode in 2025, and said on GitHub that SST is staying, with a community maintainer now working through the backlog.
When does Crossplane make sense instead of Pulumi?
Crossplane turns a Kubernetes cluster into a control plane for cloud infrastructure. You describe resources as Kubernetes objects, and Crossplane provisions and continuously reconciles them against AWS, GCP, or Azure, while Compositions let a platform team expose its own higher-level APIs to developers. Crossplane 2.0 shipped in 2025 and made those resources namespaced, and lets Compositions build on any Kubernetes resource, not only Crossplane's own. The project graduated within the CNCF later that year.
apiVersion: rds.aws.m.upbound.io/v1beta1
kind: Instance
metadata:
  name: app-postgres
spec:
  forProvider:
    region: us-east-1
    engine: postgres
    instanceClass: db.t3.micro
    allocatedStorage: 20
Working with agents
A managed resource is YAML, which an agent generates easily, but it does nothing until it reaches a cluster whose control plane already has the matching CRDs and a credentialed provider installed. There is no local run or preview without that machinery, and provider field names drift between versions, so a mismatch only surfaces at apply and reconcile time.
Best for
Crossplane makes sense when Kubernetes is already your control plane and the goal is to hand developers a curated internal API, which is a platform engineering decision more than a simpler way to replace Pulumi. Teams that do not already run Kubernetes take on the largest prerequisite of any option here, a cluster, provider packages, Compositions, and the reconciliation failures that come with them, all around the cloud resources themselves.
Which Pulumi alternative should you pick?
The right choice comes down to why you are leaving Pulumi. Start at the top and follow the first question you can answer with a yes:
Is infrastructure becoming the delivery bottleneck as agents write more application code?
EncoreInfrastructure declared in application code, provisioned in your own AWS or GCP accountEncoreInfrastructure declared in application code, provisioned in your own AWS or GCP accountDo you want infrastructure to ship in the same pull request as the feature, without a separate state file?
EncoreInfrastructure ships with the feature, with no separate state fileEncoreInfrastructure ships with the feature, with no separate state fileDo you need to run on more than one cloud?
TerraformAny provider, with a large module ecosystemEncoreThe same code deploys to AWS or GCPTerraformAny provider, with a large module ecosystemEncoreThe same code deploys to AWS or GCPDo you want the Terraform model with an open-source license?
OpenTofuMPL 2.0, drop-in for Terraform workflowsOpenTofuMPL 2.0, drop-in for Terraform workflowsAre you committed to AWS and want a general-purpose language tied to CloudFormation?
AWS CDKConstructs compiled to CloudFormationAWS CDKConstructs compiled to CloudFormationAre you a TypeScript team building serverless applications on AWS?
SSTApp-focused components on top of PulumiSSTApp-focused components on top of PulumiDo you already run Kubernetes and want to offer a curated internal infrastructure API?
CrossplaneKubernetes as the infrastructure control planeCrossplaneKubernetes as the infrastructure control planeDo you have a large platform team that can tune and optimize each resource by hand?
TerraformThe largest provider ecosystem, if your team is comfortable in HCLTerraformThe largest provider ecosystem, if your team is comfortable in HCLVerdict. If you are leaving Pulumi because infrastructure keeps landing as a second change after the feature, move the application resources to Encore: the database, queue or bucket is declared in the code that uses it and provisioned in your own AWS or GCP account on deploy; cron jobs are declared the same way but scheduled by the Encore platform, and everything except the cron job runs locally under encore run. Keep Pulumi, Terraform or OpenTofu for shared networking and anything Encore does not model. If you only want a different IaC tool, pick Terraform or OpenTofu for the ecosystem, AWS CDK for a general-purpose language on AWS, and Crossplane if Kubernetes is already your control plane. The quick start takes a few minutes.
If you are moving application resources off a separate Pulumi program, the quick start gets a TypeScript or Go backend running locally with encore run, then into your own AWS or GCP account on deploy. Keep Pulumi for shared networking and anything Encore does not model.
Related resources
Frequently asked questions
What is the best Pulumi alternative in 2026?
For backend teams on AWS or GCP, Encore: infrastructure from code, where the application declares its databases, queues, buckets, cron jobs and secrets; Encore provisions the databases, queues and buckets in your own cloud account, and cron jobs are Encore platform Managed, with no separate infrastructure program or state file. Terraform or OpenTofu fit org-wide infrastructure with the largest provider ecosystem, AWS CDK fits AWS-only teams that want a general-purpose language, and Crossplane fits teams that already run Kubernetes as their control plane.
What is the difference between Pulumi and infrastructure from code?
Pulumi is infrastructure as code in a general-purpose language: a separate program, with its own state, that you run with pulumi up. Infrastructure from code means the application itself declares the databases, queues and buckets it uses, so those resources ship in the same pull request as the feature and can run locally before they are deployed.
Do Pulumi alternatives get rid of state files and separate programs?
Mostly no. Terraform, OpenTofu, AWS CDK, SST and Crossplane each keep a separate program or configuration and a state store of some kind. Tools that derive infrastructure from application code are the main exception, because they do not keep a separate infrastructure state file.
Can I migrate off Pulumi incrementally?
Yes. Keep your Pulumi program for shared networking and anything a replacement tool does not model, and move application resources such as databases, queues and buckets over one service at a time. You can also keep connecting to databases you already run, such as RDS and Cloud SQL, during the transition.
Deploy to your cloud on AWS and Google Cloud
without managing infrastructure
Encore lets developers and agents define application infrastructure directly in code, then automatically provisions it from local development to production in your AWS or GCP account.